 Mini-Module
Summary
The Advanced Linux/Unix System Security module is designed for detection engineers specializing in identifying and responding to cyber threats, Cybersecurity experts and enthusiasts seeking advanced knowledge in detecting and mitigating cyber threats, and Advanced Linux/Unix users and network administrators looking to enhance system security. Throughout this module, students will develop advanced Cyber Attack Detection: Develop expertise in recognizing and mitigating sophisticated cyber threats in Linux and Unix systems and robust Security Configuration: Learn to implement advanced security configurations to fortify your digital assets against vulnerabilities.
Recommended prior knowledge:
- Completion of a foundational Linux/Unix system security module or equivalent knowledge in the field
- Familiarity with basic cybersecurity concepts, including threat detection and incident response
Linux Log Infrastructure
The Linux operating system provides a good amount of information about how the system works and what type of events occur. Log files store important information about the system which provides in-depth information about it. In this training, we will learn about the Linux log engine, various log files and how you can use them.
For any Linux system administrator or security professional, log files are an indispensable tool for identifying errors, monitoring system events, and detecting security issues. However, to be able to use the information provided by these files effectively requires certain knowledge and skills.
This training will help you gain a deep understanding of the Linux log engine and teach you how to use these powerful tools. You will learn where the log files are located, how to read and analyze them, what information they contain and how to manage log files. We will also cover topics such as rotation of log files and the use of log analysis tools.
Importance of Log Files
Linux log files give system and network administrators detailed information about what is happening on a system. Examining the log files of various services and applications is often an important step when administering a Linux system.
We can collect the importance of Linux log files under the following headings:
Debugging
Log files are often the first place to look to understand why a service or application is not working properly. Log files are often helpful in finding causes and solutions to errors.
Security Auditing
Log files are used to detect suspicious or malicious activities. This may include login attempts, unauthorized file access, or system changes.
Performance Monitoring
Log files provide information about the performance of a system. For example, you can see how quickly a service responds or how long a transaction takes to complete.
System Maintenance
Log files allow you to monitor events on a system over a long period of time. This can help system administrators plan maintenance requirements, anticipate unexpected events, and intervene as needed.
For these reasons, checking log files regularly and taking action when necessary is an essential part of keeping a Linux system safe and running efficiently.
Locations and Functions of Log Files
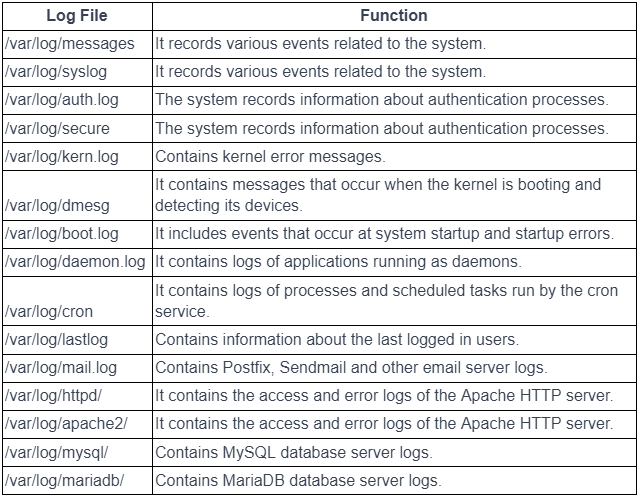
Locations and functionality of log files may vary depending on distribution and configuration. The table below contains commonly used log files. If you are using a different Linux distribution or your system configuration has changed, it is important to verify the location and name of the log files.
Reading and Understanding Log Files
Reading and understanding Linux log files is an essential skill for system administrators and security professionals. Log files help monitoring system status, analyze errors and examine security events by recording events that occur during system operation. Below are important steps for reading and understanding Linux log files:
Log File Location
We first need to determine the location of the log files that we need to read and review. In addition to the locations of the log files mentioned above the "/var/log" directory is another important location where the common log files are usually stored.
Reading Log File
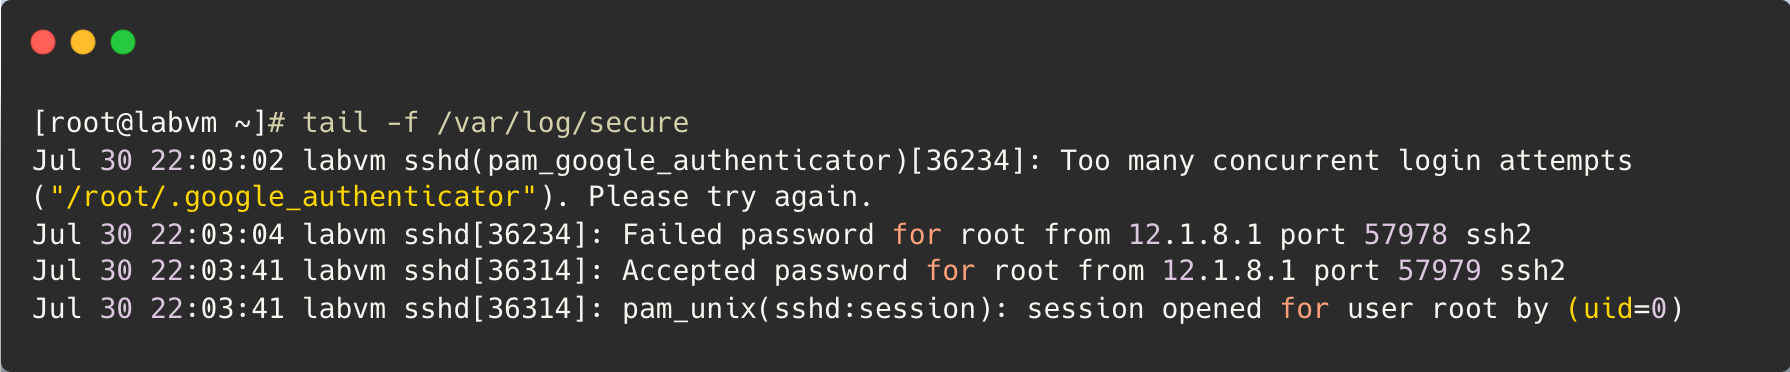
You can use "less" or "tail" commands in the terminal to open a log file. For example, you can open the "syslog" file with the command "less /var/log/syslog". With the “tail -f /var/log/messages” command, you can follow the file continuously and see the newly added logs instantly.
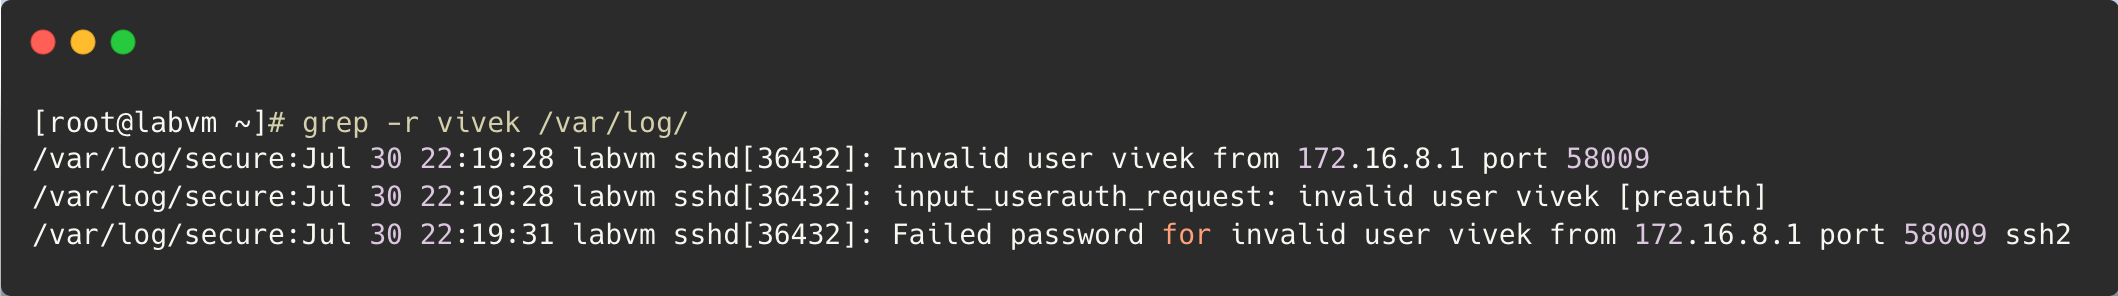
The “/var/log” directory may contain many log files and directories where logs of applications are stored. We can use the "grep" command, where we can search for string expressions in the files if we are not sure where to search for data (IP address, domain, username, etc.).
For example, let's search for user "vivek" in all log files:
-r parameter: It is also used to search for files in directories.
In this part of the training, we have covered the log infrastructure in Linux, the importance of log files, the locations and functions of log files, and how to read log files. We will learn about the Syslog and Rsyslog topic in the next part of our training.
