 Mini-Module
Summary
The Linux Memory Forensics module is designed for
- Cybersecurity professionals, - Digital forensic analysts, and
- Incident responders. Throughout this module, students will develop
- Proficiency in extracting and analyzing memory dumps from Linux systems using various tools and techniques, - Understanding of memory structures, processes, and artifacts specific to Linux environments, - Ability to identify and interpret volatile data such as running processes, network connections, and system configurations stored in memory, and
- Skills to employ advanced memory forensics methodologies to uncover hidden or obfuscated evidence in Linux memory dumps.
Recommended prior knowledge:
-
Basic understanding of Linux operating system fundamentals
-
Familiarity with command-line interfaces (CLI) in Linux
Introduction to Linux Memory Forensics
In the ever-evolving landscape of the digital age, cybersecurity and forensics have become more important than ever. In this fast-paced environment, "Memory Forensics", or memory forensic analysis, has emerged as an indispensable tool in the investigation of cybercrimes and security breaches. Developing memory forensics skills, especially on systems running Linux operating systems, allows professionals to more effectively identify, analyze, and mitigate these threats.
Memory Forensics involves the examination of a system's physical memory (RAM). This is vital to understanding what a computer is currently doing or has done in the past. In the event of a system crash, malware infection, or other security breach, the data stored in RAM can be extremely valuable information. The Linux Memory Forensics module provides a comprehensive guide to accessing, analyzing, and reporting this valuable information.
Memory forensics is primarily used for malware analysis, debugging, analyzing system performance issues, detecting data leaks, and monitoring user activity. It is also critical for root cause analysis of system crashes and understanding of attackers' actions during a security breach.
Required Tools
LiME (Linux Memory Extractor) and Volatility for Linux Memory Forensics are essential tools that are widely used for memory analysis. The purpose and use of each tool is described in detail below:
LiME (Linux Memory Extractor)
LiME is a tool designed for use in Linux operating systems to create a secure copy of the system's RAM. It works as a kernel module and can export the contents of memory in various formats (e.g. raw, lime format) to a disk file.
LiME is used during forensic analysis and security investigations to collect data from system memory. This includes valuable information about running system processes, network connections, user sessions, and even potentially malicious software. LiME allows retrospective analysis of events that occurred while the system was down or active by creating a complete and unaltered copy of the data.
Features of LiME:
-
Hash of dumped memory
-
Acquisition via network interface
-
Minimal process footprint
-
Full Android memory capture
LiME can be installed on Ubuntu Linux distribution as shown in the screenshot below. These commands will create the required LiME module for the system. In Linux, the module is used for memory dumping.
The 'lime' repository is downloaded.
[!bash!]$ git clone https://github.com/504ensicsLabs/LiME.git
You change to the 'lime/src' directory.
[!bash!]$ cd LiME/src/
The code is compiled with the make command.
[!bash!]$ make
The 'lime' is searched for within the kernel modules using the lsmod command.
[!bash!]$ lsmod | grep -i lime
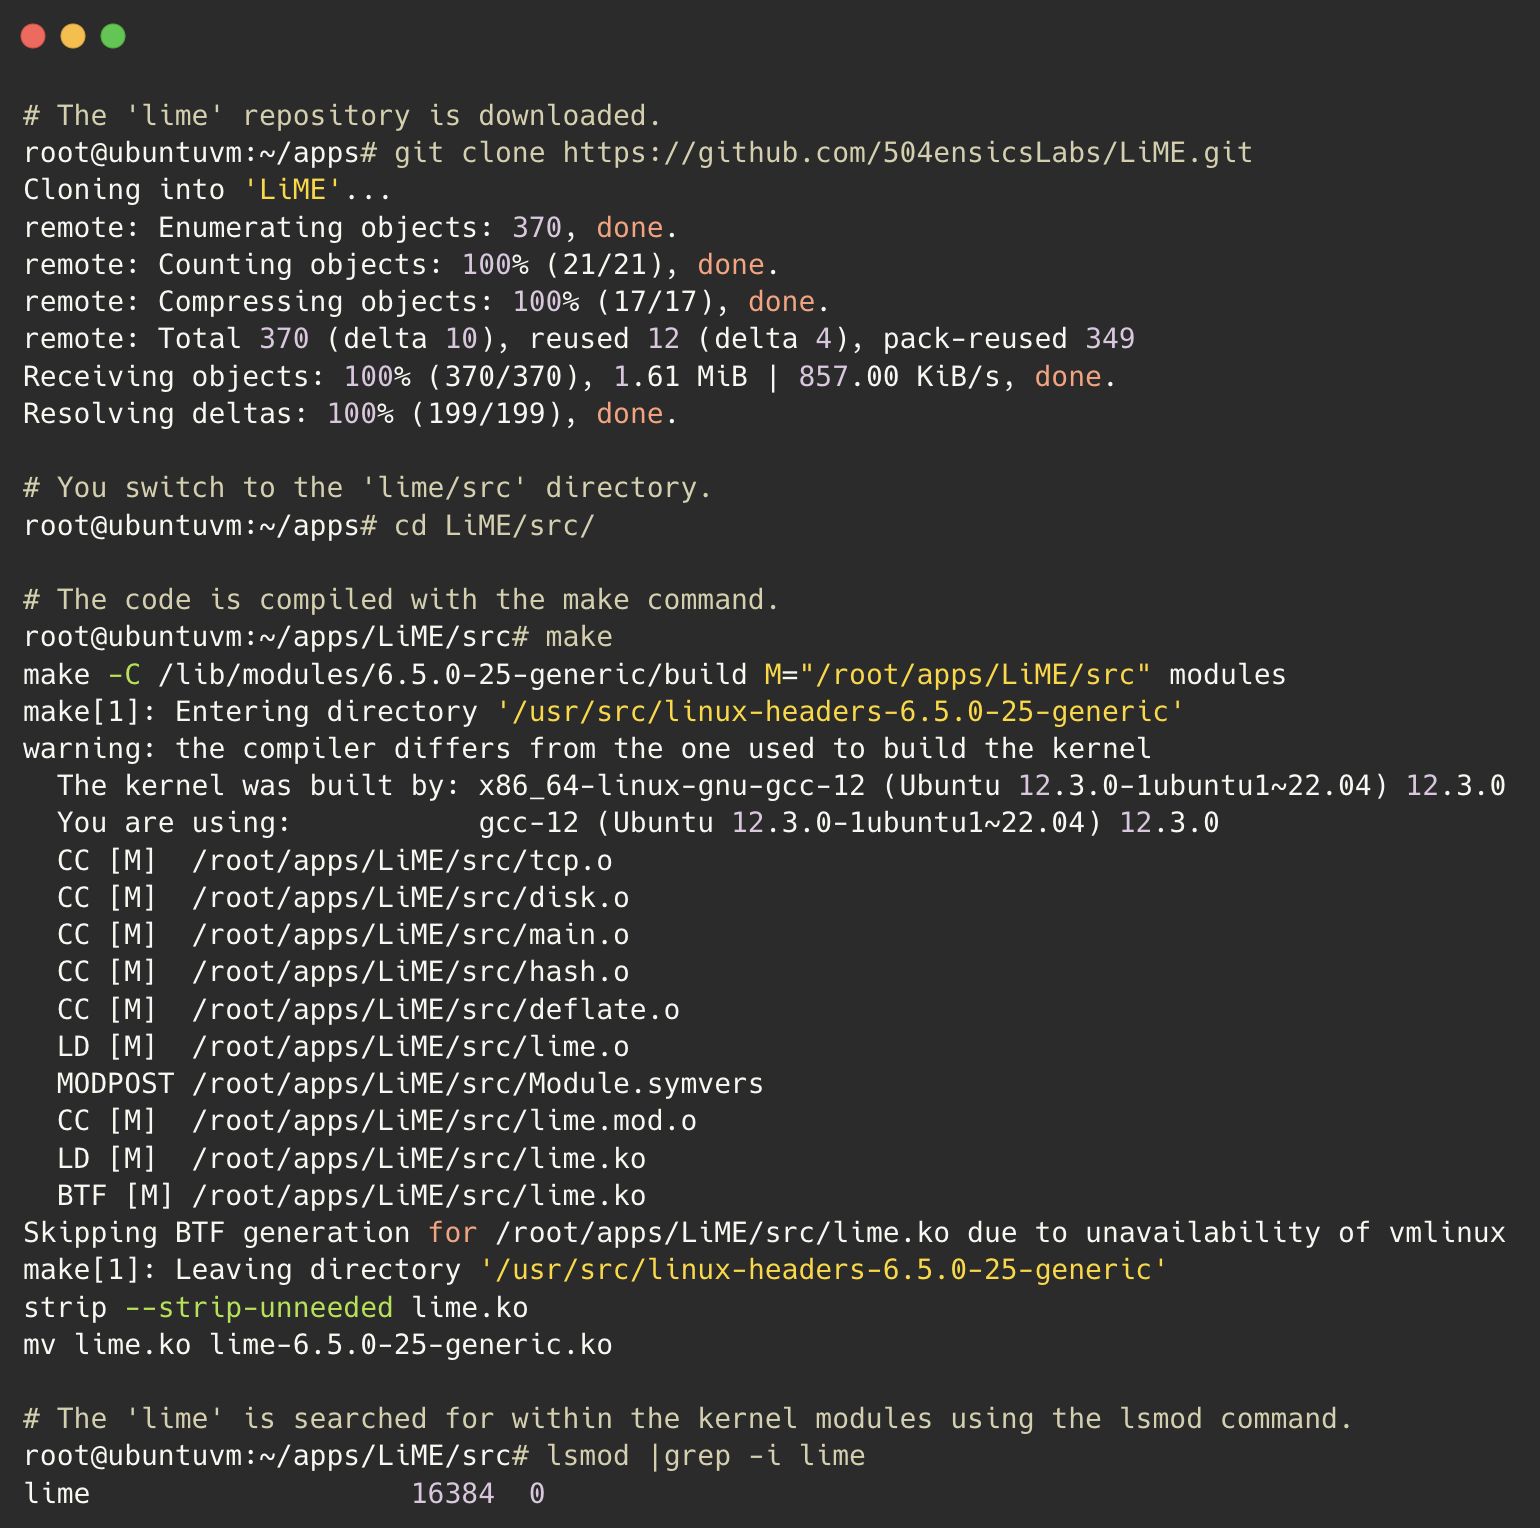
This concludes the Linux LiME installation and the Linux LiME tool is ready to use. We will explain how to use it in the next sections.
Volatility
Volatility is an open-source memory analysis framework. It is available for both Linux and Windows environments. Volatility is a powerful tool for analyzing the information contained in the RAM of operating systems. Compatible with a wide range of operating systems and memory dump formats, Volatility provides a comprehensive framework for memory analysis. It is written in Python and has an extensive library of plug-ins.
Volatility is used to analyze memory dump output from tools such as LiME. It allows users to list processes in RAM, DLLs, network connections, open files, registry keys, and more. It is also used to detect malware, reveal hidden codes, and examine general user activity on the system. Volatility is one of the most widely used memory forensics tools and is essential for performing detailed memory analysis.
Volatility supports several sample file formats and can convert one to another. The supported file formats are listed below:
-
Raw linear sample (dd)
-
Hibernation file (from Windows 7 and earlier)
-
Crash dump file
-
VirtualBox ELF64 core dump
-
VMware saved state and snapshot files
-
EWF format (E01)
-
LiME format
-
Mach-O file format
-
QEMU virtual machine dumps
-
Firewire
-
HPAK (FDPro)
Installing Ubuntu 22.04 Volatility3 can be done as shown below.
Python3 or higher is required to use Volatility3.
The latest version of Volatility is downloaded from the official repository.
[!bash!]$ git clone https://github.com/volatilityfoundation/volatility3.git
You change to the 'volatility3' directory
[!bash!]$ cd volatility3/
Run "python3 setup.py build" command
[!bash!]$ python3 setup.py build
Run "python3 setup.py install" command
[!bash!]$ python3 setup.py install
To install the most minimal set of dependencies use a command such as
[!bash!]$ pip3 install -r requirements-minimal.txt
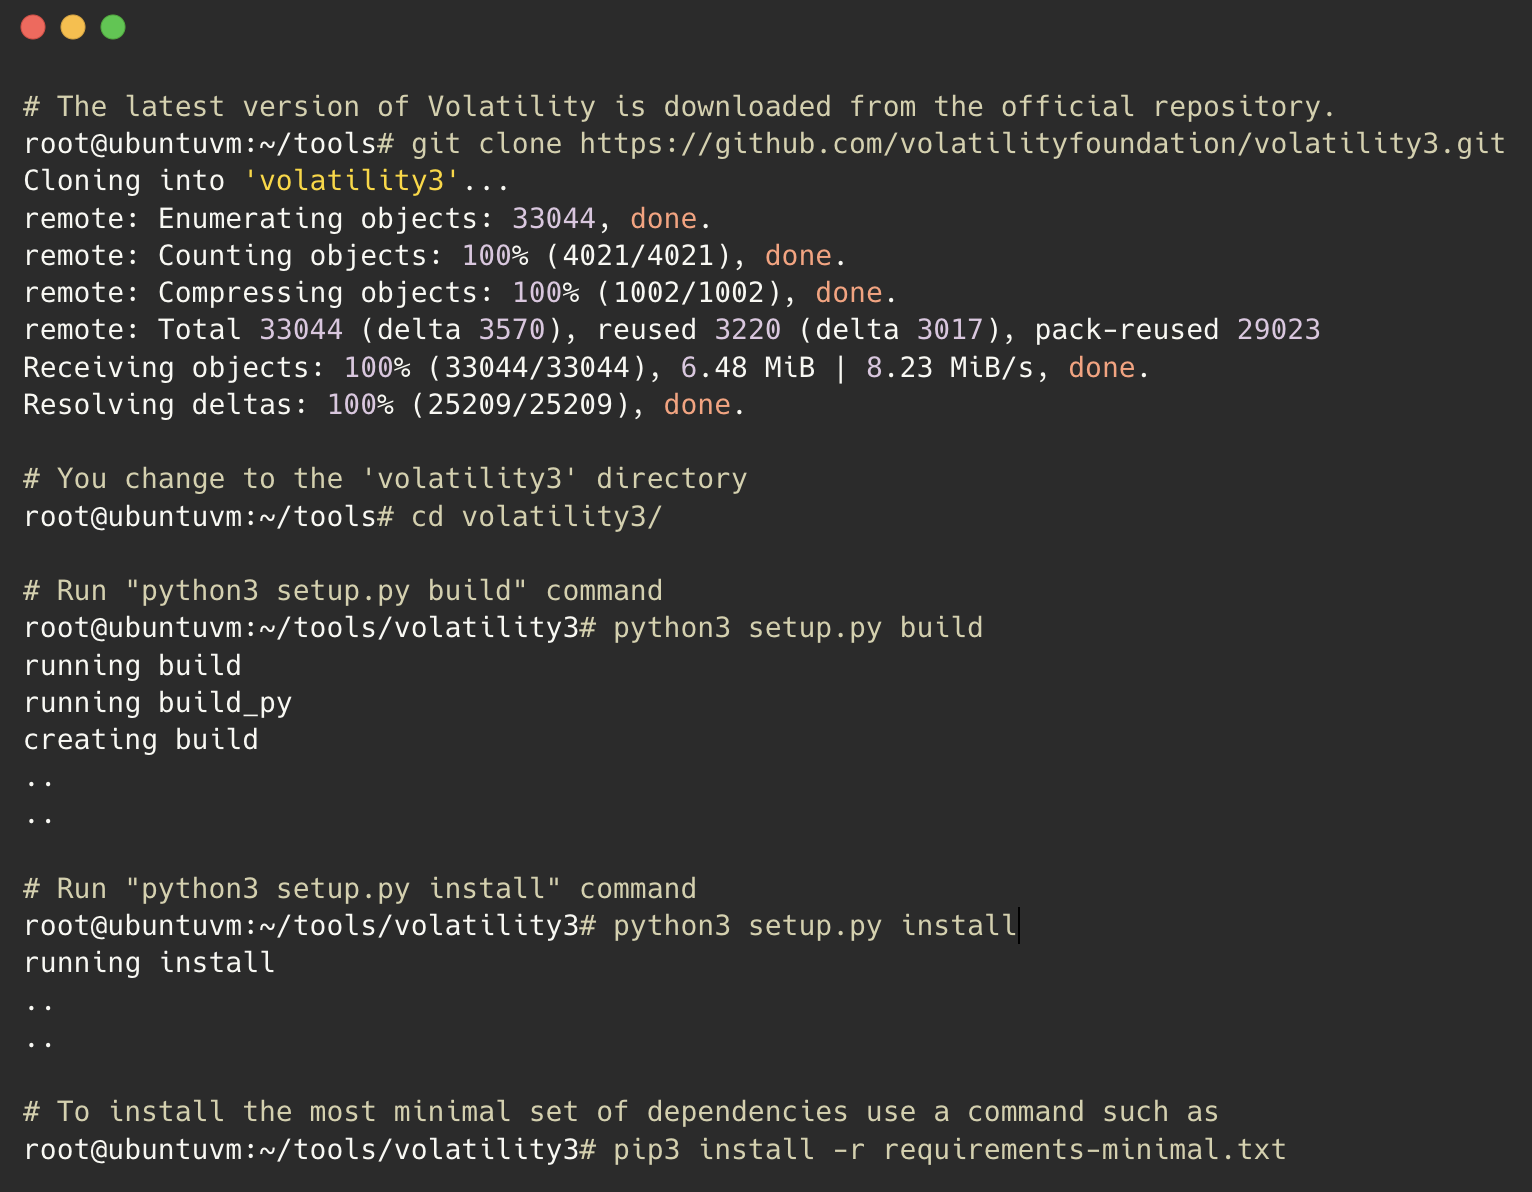
The installation of Volatility3 is now complete and the tool is ready for use. We will explain how to use Volatility3 in the next sections.
Conclusion
In the digital age, cybersecurity, and forensics have become increasingly important, and memory forensics has become a fundamental tool for analyzing cybercrimes and security breaches, especially on Linux systems. At its core, LiME is a memory dump collection and analysis tool that securely retrieves valuable data from system memory, while Volatility provides detailed analysis of that data. Both tools are valuable resources for forensic analysts and are used in a variety of areas including malware detection, debugging, and user activity monitoring. Effective use of these tools allows for more detailed and accurate forensic analysis.
In the next section, we will discuss creating a memory dump using the LiME tool.
