 Mini-Module
Summary
The Phishing Email Analysis module is designed for security professionals seeking to enhance their skills in threat detection, Network administrators and email system managers, Business professionals responsible for company data protection, Anyone interested in entering the field of cybersecurity, and Individuals aiming to increase their awareness and safety from phishing attacks. Throughout this module, students will develop an understanding of the fundamental concepts and techniques used in phishing attacks, the ability to systematically analyze and identify phishing emails, proficiency in utilizing tools and technologies for email analysis, to implement effective countermeasures to safeguard against phishing threats, and enhanced your organization’s email security and educate others on safe email practices.
Recommended prior knowledge:
- Familiarity with cybersecurity concepts is beneficial but not mandatory
Introduction to Phishing
A phishing attack is a type of attack that usually aims to steal the user's personal information by tricking them into clicking on malicious links in emails or running malicious files on their computer.
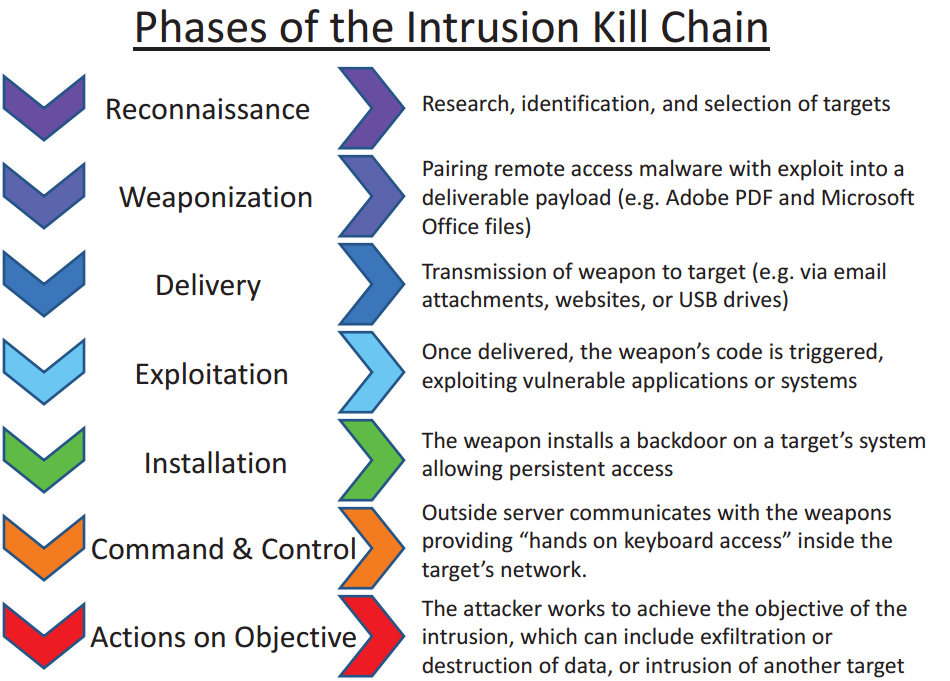
Phishing attacks fall into the Delivery phase of the Cyber Kill Chain model created to analyze cyber-attacks. The 'delivery' phase is where the attacker transfers the pre-arranged malicious content to the victim systems/people.
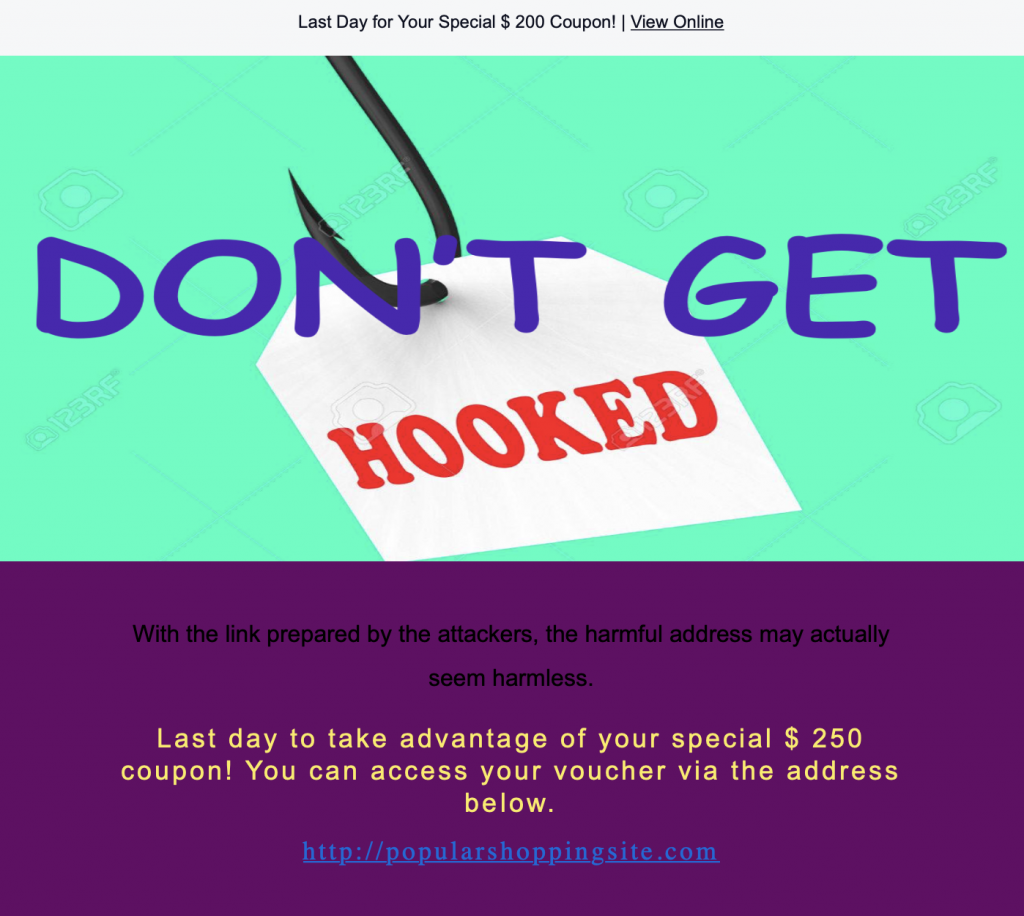
The attackers usually aim to get victims to click on the malicious link in the email by using tricky phrases such as "you have won a gift", "don't miss out on the big discount", "if you don't click on the link in the email your account will be suspended".
Phishing is the most common initial attack vector.
[Twitter](https://twitter.com/intent/tweet?text=The phishing attack is the most common attack vector for initial access. @LetsDefendIO https://app.letsdefend.io/academy/section/Phishing-Attack/) Linkedin Facebook
Of course, the purpose of the attack is not to steal the user's password information, but to exploit the human factor, the weakest link in the chain. Attackers use phishing attacks as a first step to infiltrate systems.
