 Mini-Module
Summary
The Wazuh module is designed for security analysts and incident responders looking to expand their knowledge and skills in threat detection and response, Individuals interested in pursuing a career in cybersecurity and seeking foundational knowledge in security monitoring and threat detection, IT professionals and system administrators interested in learning about open-source security platforms and SIEM processes, and Anyone interested in gaining a comprehensive understanding of the Wazuh Open Source Security Platform and SIEM processes for personal or professional development. Throughout this module, students will develop comprehensive understanding of the Wazuh Open Source Security Platform, proficiency in installing and configuring Wazuh in a lab environment, practical knowledge and experience in log collection, parsing, and analysis, ability to write rules and correlations for effective threat detection, and skill in detecting and responding to security incidents using Wazuh.
Recommended prior knowledge:
-
Basic understanding of computer networks and network security concepts
-
Familiarity with operating systems such as Linux and Windows
-
Experience with log analysis and familiarity with common log formats
-
Familiarity with security tools and technologies commonly used in the industry
Introduction to Wazuh
Wazuh is an open-source cybersecurity platform. The Wazuh project started as a fork of Ossec-HIDS in 2015 and completed many important shortcomings with the additional features in time and become a comprehensive cyber security solution.
Wazuh now includes many SIEM (Security Information and Event Management) and XDR (eXtended Detection and Response) capabilities, and that's why it's called a cybersecurity platform, not just SIEM or XDR.
The following list will give you some insights and summarizes Wazuh’s capabilities as a complete cybersecurity platform:
-
Collection, correlation, and analysis of security events.
-
File integrity monitoring (FIM).
-
Malware and rootkits detection.
-
Security configuration assessment (SCA).
-
Agent-based vulnerability detection.
-
Security monitoring for cloud-native applications, containers and Kubernetes.
-
Threat detection for SaaS solutions and cloud providers.
-
MITRE ATT&CK and regulatory compliance mapping.
-
Automated responses to detected threats.
Note: End of the module (Sample Attack Scenarios) you'll practice incident investigation with Wazuh.
How to Connect to the Wazuh Lab?
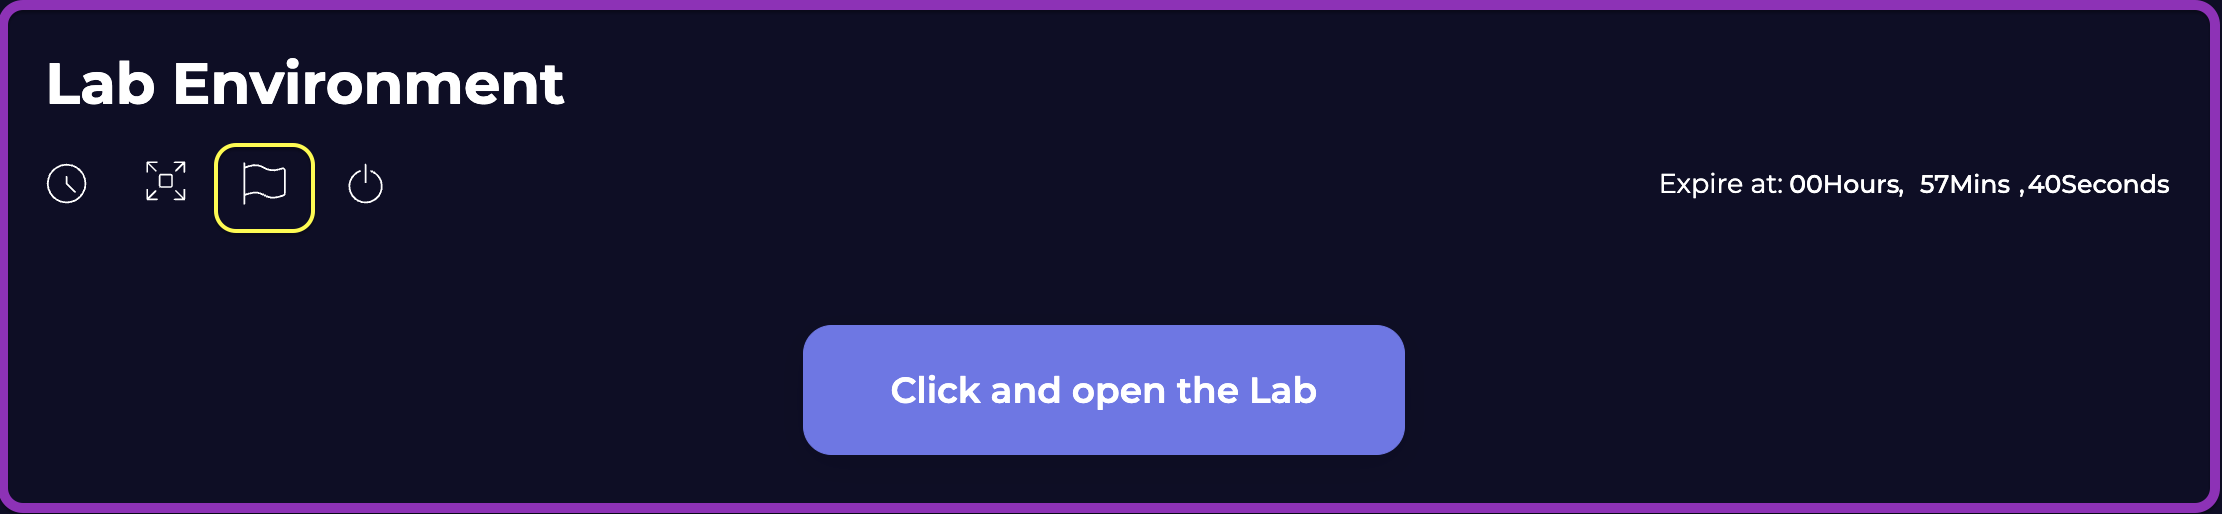
1- Click the connect button and wait for the deployment (About 3-4 minutes)
2- After the button appears, click it
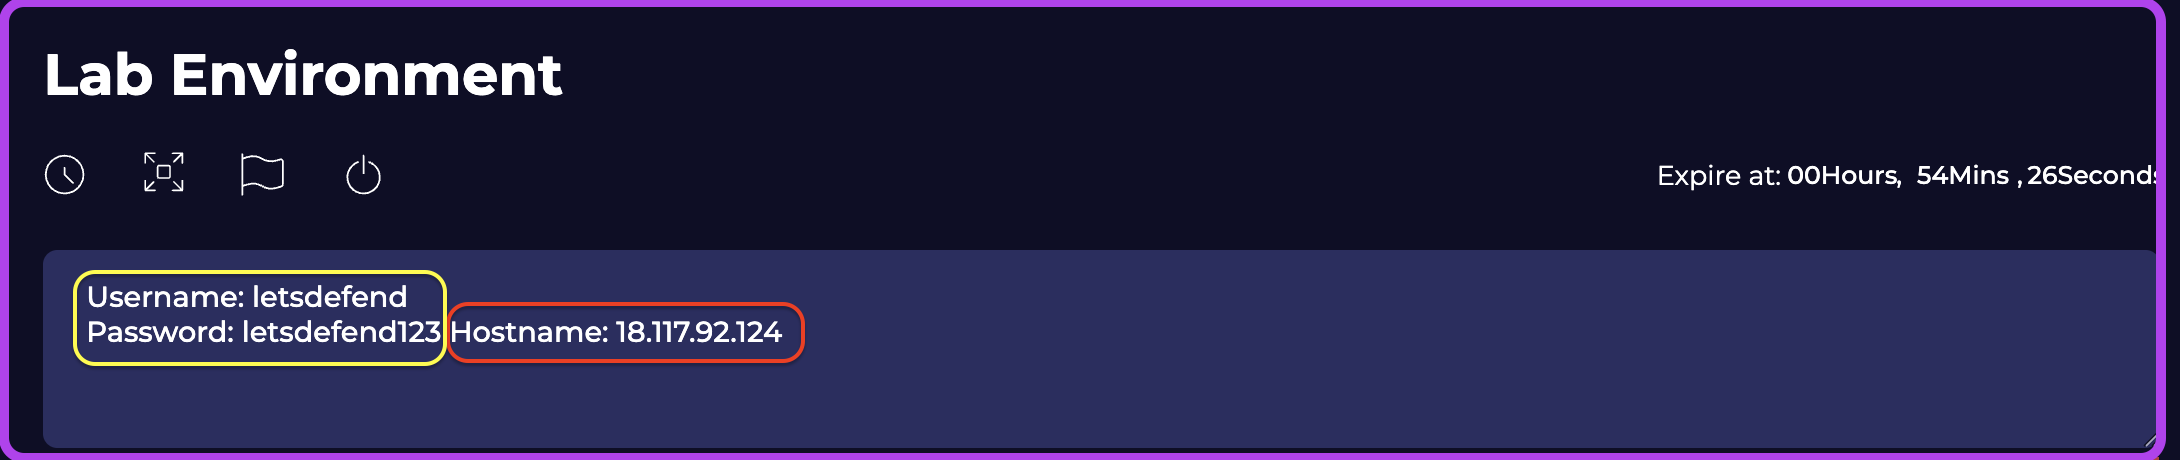
3- Go to https://IP-Address on your browser
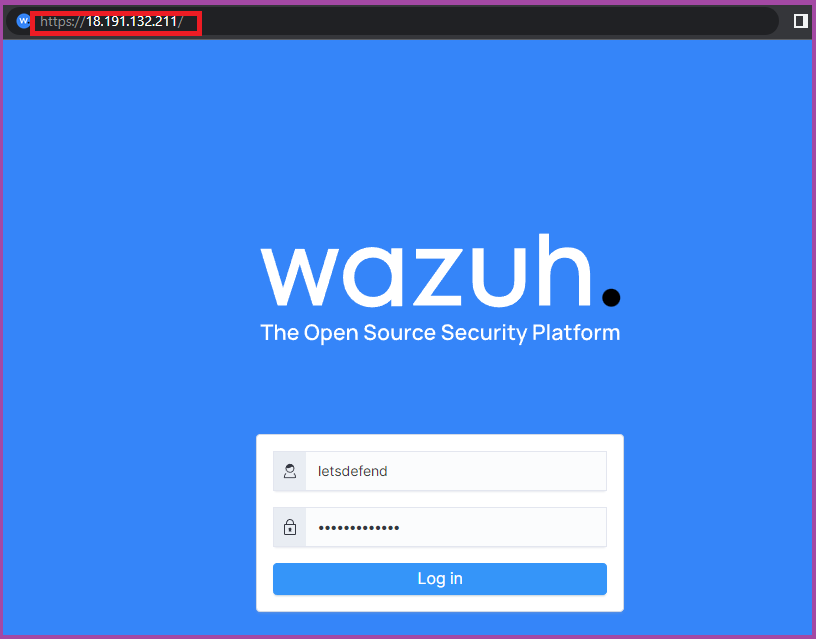
4- Put the credentials (letsdefend:letsdefend123)
